A cloud foundation the team understands
Clear environments, ownership, IAM boundaries, networking, and documented operating decisions.
GCP for startups and small teams
I help growing teams turn product requirements into secure, automated, observable Google Cloud infrastructure without adding unnecessary platform complexity.
What changes
Clear environments, ownership, IAM boundaries, networking, and documented operating decisions.
Terraform and controlled CI/CD make infrastructure reviewable, reproducible, and easier to recover.
Useful logs, metrics, alerts, request tracing, and runbooks are included in the platform design.
Budgets, scaling limits, service choices, and cost tradeoffs are made visible before deployment.
Focused engagements
Each engagement produces practical decisions, prioritized findings, and implementation evidence your team can continue using.
Assess projects, IAM, networking, environments, delivery, security, reliability, and cloud spend.
Build reusable infrastructure, validation gates, keyless GitHub delivery, and an approval-based plan/apply workflow.
Define service indicators, alerts, dashboards, incident paths, backup expectations, and operational evidence.
GCP startup readiness checklist
Unchecked items are useful discussion points, not a score of failure. The right controls depend on the workload, data, risk, and stage of the business.
Implementation evidence
The case study documents Cloud Run, private Cloud SQL, keyless GitHub delivery, policy-checked Terraform, request-level observability, and budget alerts.
Review the case study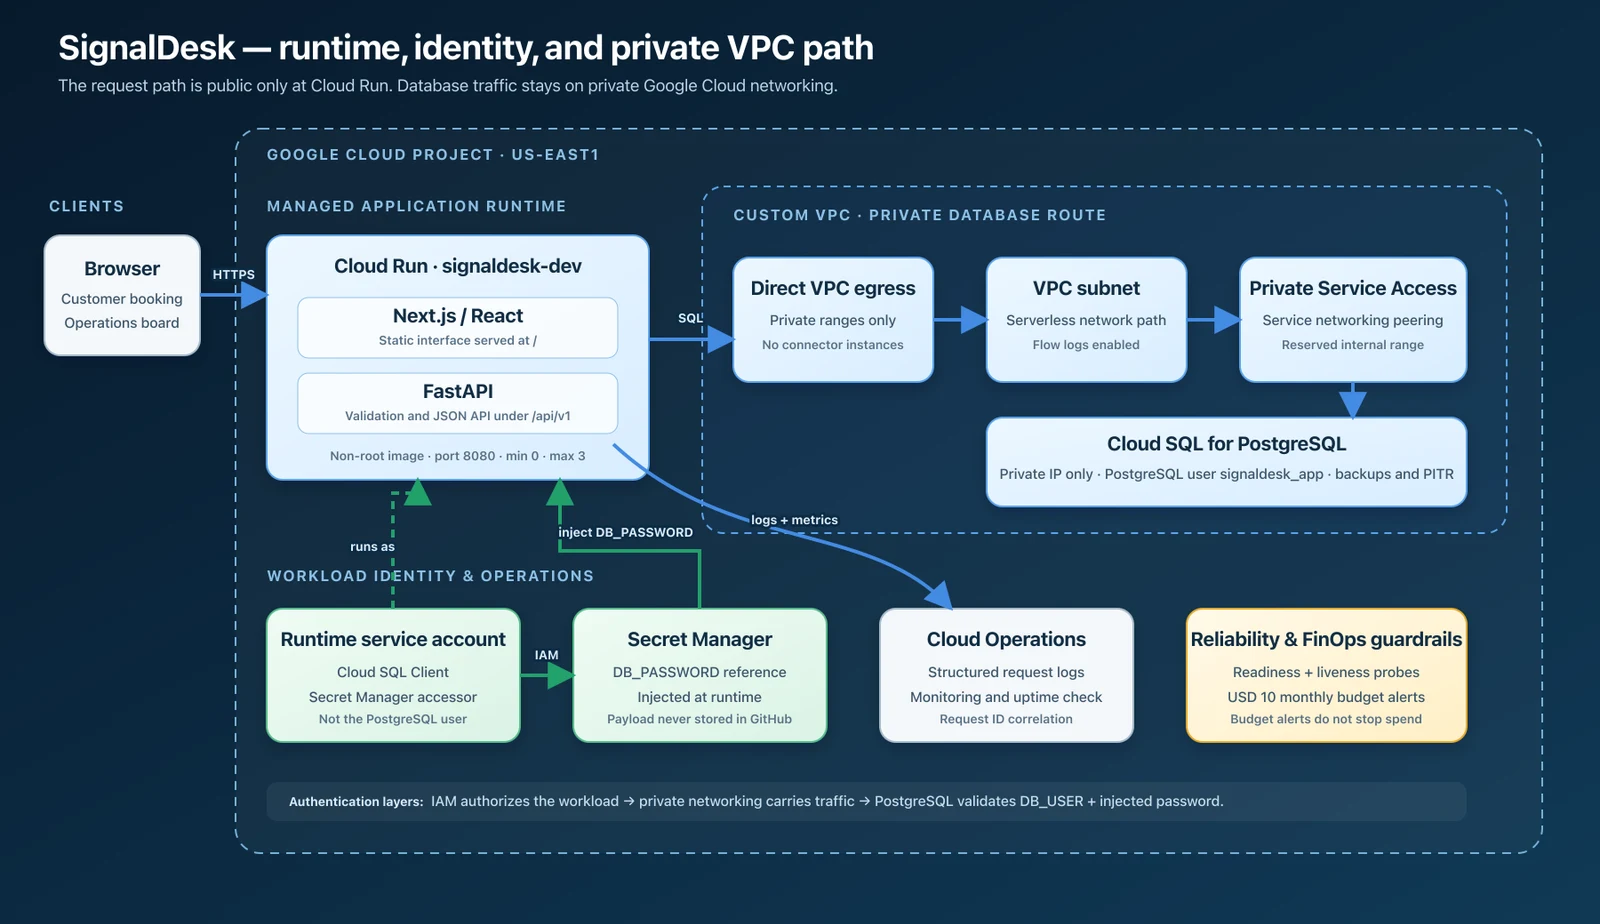 Review source on GitHub
Start with clarity
Start with the workload and the team's operating capacity. Cloud Run suits many containerized web applications without requiring cluster management. GKE makes sense when Kubernetes capabilities justify that added responsibility. The SignalDesk case study explains why I chose Cloud Run and what that choice gives up.
Begin with repeatable foundations: projects, service identities, permissions, networking, and the runtime. Keep state protected, review the actual plan, and define which resources Terraform owns before connecting application delivery.
Estimate baseline database and networking costs, set service scaling limits, and assign a cost owner. Add budget alerts early, but do not treat them as a hard spending cap. Review actual usage after deployment.
Your current architecture or product requirements, data sensitivity, expected traffic, recovery needs, and a realistic budget. We can use those constraints to identify the next useful change. Discuss your GCP project.